DPO Radio
AESIRX COMPLIANCEONE
Follow the legal issue from its source to the next reviewed action.
Deploy on firm-controlled infrastructure, manage supported AI configuration and use your firm’s own API key (BYOK). Connect client engagements, private Matters, cited research and reviewed work in a dedicated law-firm application.
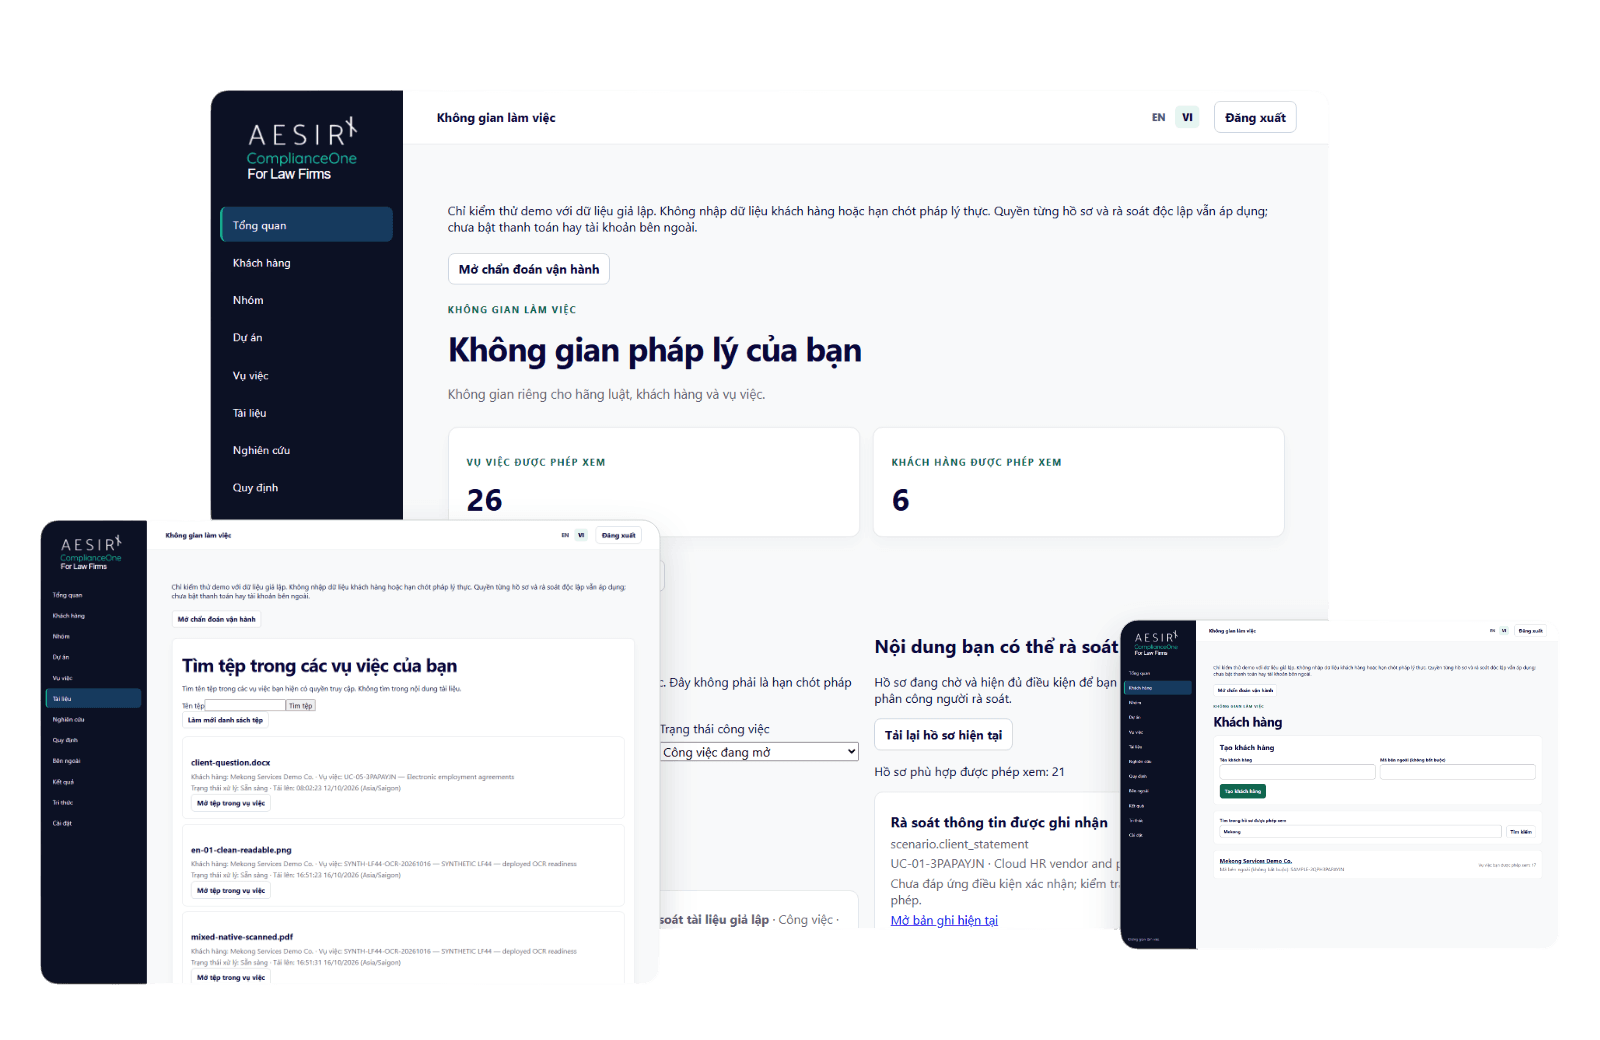
A client engagement can involve several legal issues, practice teams and deliverables. Lawyers need to coordinate the work while keeping each private Matter’s documents, sources and members clear.
The difficult handoffs often happen between research and drafting, or between planning and the next person’s task. Missing facts, unclear source versions and informal review decisions can be lost when work moves through disconnected folders and messages.
ComplianceOne for Law Firms connects these activities around named records. Staff can inspect evidence, preserve unknowns, review source-bound work and open the next permitted task without assuming that one role grants every kind of access.
This is a separate Law Firms application within the ComplianceOne product family. Its available workflows depend on the agreed deployment, current configuration, record membership and source rights. The workspace supports professional review; it does not replace legal judgment or the firm’s rollout approvals.
Client information needs deliberate choices about hosting and processing. ComplianceOne for Law Firms supports a separate deployment with AI configuration and provider accounts managed by the firm.
Under an agreed self-hosted configuration, the application and documents run on the firm’s infrastructure. Identify the appropriate hosting environment and agree access, backup and operating responsibilities before introducing actual client material.
Authorized staff can configure the supported provider, model and compatible options, then choose a default for Forseti work. The firm can assess the available AI service against its information-handling requirements.
Bring Your Own Key (BYOK) here means using an API key from the firm’s AI-provider account. The firm manages the account and connection configuration. Saved credentials are encrypted and are not displayed back through the settings interface.
When an AI task runs, the connected service receives the content needed for the request. Processing location, retention and use for training depend on the provider and account arrangements. Assess both hosting and the connected AI service before using client documents.
 Client Management for Law Firms
Maintain named client records and open permitted engagement work in ComplianceOne for Law Firms.
Private Legal MattersKeep named members, structured facts and recorded responsibility together around one legal issue.
Evidence and Document ReviewFind permitted files, inspect processing coverage and compare supported PDFs with their original pages.
Cited Research with ForsetiResearch a named Matter with permitted evidence and inspect the passages behind the assistant’s proposals.
Legal Sources and UpdatesBrowse installed references and govern firm imports, source checks and explicit Matter source selections.
Dossiers and Reviewed Work ProductsAssemble internal dossiers, revise attributed work and export permitted versions with their source context.
Firm Knowledge and TemplatesPublish selected firm material and use approved knowledge or template versions within current access.
Practice TeamsMaintain practice rosters and scoped planning roles while preserving separate private Matter access.
Engagement Projects and PlanningOrganize tasks, dates and delegated leads around client engagements and their named Matters.
Daily Caseload and Personal WorkPrioritize permitted Matters, personal planning assignments and records currently available for review.
Controlled Client AccessExplore recipient-specific disclosure and supporting-input workflows separate from staff access.
Time Records and Invoice DraftsRecord permitted actual time, inspect rate policies and review internal invoice drafts.
Administration and IntegrationsInspect workspace readiness and configure supported providers, access and selected-source connections.
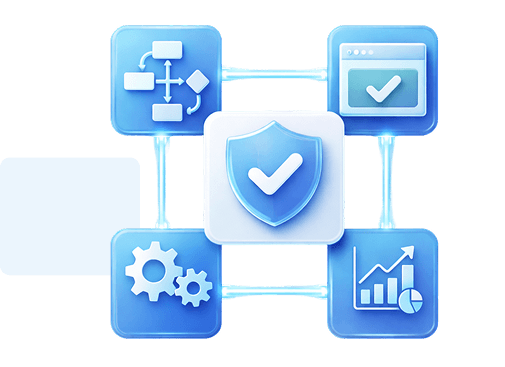
Start with the named client and engagement, then open the specific private Matter. Inspect its evidence, propose meaningful facts and research the question against permitted sources.
Carry the findings into an internal dossier or work product for review, while native planning and daily work keep the next recorded action visible.
Client disclosure remains a separate decision about selected reviewed material and a named recipient. Planning estimates, actual time records and internal invoice drafts also retain their distinct purposes.
Use an agreed synthetic demonstration to evaluate the roles, evidence and handoffs that matter to your firm.
Ronni K. Gothard Christiansen - Technical Privacy Engineer & CEO
Technical Compliance Expert, 32+ Years Open Source Advocate, X-BoD Open Source Matters Inc.
ComplianceOne for Law Firms is a separate application in the ComplianceOne product family. Its client, Matter and recipient workflows have their own current configuration and record-access boundaries; main-GRC access does not automatically transfer into them.
Forseti supports cited research and proposals for professional review. Lawyers must inspect the sources, missing facts and current context; a generated answer or exported draft is not an independently verified legal conclusion.
The library distinguishes installed references, governed imports and configured document checks. A successful check covers its configured source and does not establish complete government-portal monitoring, legal effect or applicability to a client.
Internal export and client disclosure are distinct. Staff must use the available named-recipient, source-rights, confidentiality and review controls for the exact selected material before explicitly sharing it.
Start with synthetic records and representative staff roles in an agreed evaluation deployment. For self-hosting and API-key BYOK, confirm infrastructure, the provider account, supported AI settings and data-handling arrangements. Retain the firm’s independent legal, security and operational approval requirements before introducing actual client work.

Test connected legal workflows, access controls and review processes using synthetic client Matters.

Discuss your firm’s hosting, AI configuration, data handling and legal workflow requirements.

The evolution of Aesir is Aesir +  (the Norse symbol for Necessity)"Needed in order to achieve a particular result"
♥Join the AesirX Privacy Newsletter. Stay Informed. Stay Compliant.