DPO Radio
ACTIVE
Decision 1964/QĐ-TTg — Cybersecurity Assurance Index
Read the Index's criteria, weights and scoring method beside your own cybersecurity evidence. Any organisation may use the Index to assess itself. Index results come from the assessing State bodies and are consolidated by the Ministry of Public Security; a self-assessment is not one.
Decision 1964/QĐ-TTg of the Prime Minister issues the Cybersecurity Assurance Index (Chỉ số bảo đảm an ninh mạng). It was signed on 12 October 2026, on the proposal of the Minister of Public Security, and took effect on signature (Article 5).
Who it binds. The Ministry of Public Security runs the Index as the standing body (Article 4(1)). Ministries, ministerial-level agencies and provincial People's Committees pilot it in 2027–2028. Each assesses the information systems in its management scope, including those of its subordinate units, and reports to the standing body (Article 2(1), Article 4(2)). Provincial police advise the provincial People's Committees (Article 4(3)).
Everyone else may use it. Any other agency or organisation may study the Index and organise its own assessment (Article 2(1)). Such an organisation joins no pilot, reports to no one and is ranked nowhere. The Decision places no duty on a private organisation's own systems.
A pilot scale, not a standard. The Decision says its scales are a self-assessment scale for the pilot, not a mandatory technical regulation or standard (Appendix III). Reaching a Mức is not a legal duty for anyone, State bodies included. The Index uses two scales: a system's security level (cấp độ 1–5) under the Cybersecurity Law and Decree 331, and the Mức (0–3) each assessment item receives.
What happens next. The phases below are the Decision's own. None is a deadline for your organisation.
Results. Index results are kept confidential. Where they contain state secrets, the Law on Protection of State Secrets applies (Article 3(1)). Pilot results refine the Index and are not published or ranked (Article 3(1)–(3): publication is provided only for official results). If official application is decided, official results would be consolidated, published and ranked before May each year (Article 3(3)).
The Decision states no sanction and sets no reporting period of its own. State bodies report by the deadlines the standing body's guidance sets, and no such guidance had been found when last checked on 27 October 2026.
The Cybersecurity Law 116/2025/QH15 is one of the bases the Decision cites. It is also the law under which an assessed system's level is determined. The Decision measures; it does not detail any article of the Law.
Decree 331/2026/NĐ-CP is what Group I (Nhóm I) scores. The first two criteria ask whether a system's level-proposal dossier was approved and whether its level-based cybersecurity plan is fully deployed. Both come from Decree 331: the level criteria, the dossier and the plan. Decision 1964 scores them. It does not create the duty to hold them.
Dossiers approved before 12 October 2026 still count, for the Index. A level dossier approved before the Decision took effect remains the basis of the assessment until it is reviewed, adjusted or re-approved (Article 2(1)). That holds whatever instrument approved it, Decree 85/2016/NĐ-CP included. It says nothing about whether the level itself is still held. That question belongs to Article 45(1) of the Cybersecurity Law and Article 39 of Decree 331.
It is not Decree 343/2026. Decision 1964 does not cite Decree 343/2026/NĐ-CP on cyber-conflict response, and the two are unrelated. The national standard TCVN 14423:2026 is named as the core basis of the criteria. ComplianceOne cites it by that designation only, as an external reference. None of its content is reproduced, no requirement in ComplianceOne is built on its text, and a Mức reached in a self-assessment is not a statement of conformity with it.
| Group | Criteria | Weight in the Index | Applies to |
|---|---|---|---|
| Group I (Nhóm I) — general compliance | 2: I.1 level dossier (weight 5), I.2 level-based plan (weight 10) | 20% | Every information system |
| Group II (Nhóm II) — specific criteria | 18: II.1 to II.18 | 80% | Systems at level 3 and above. II.13 applies only from level 4. II.16 applies only where software is developed. Some items apply only at level 4 or 5 |
| Group III (Nhóm III) — direction and management | 9 statistics: III.1 to III.9 | 0%, not counted | Every information system |
| Code | Criterion | Weight |
|---|---|---|
| II.1 | Cybersecurity risk management | 10 |
| II.2 | Hardware asset management | 9 |
| II.3 | Software asset management | 9 |
| II.4 | Information asset management | 10 |
| II.5 | Secure configuration of hardware and software | 10 |
| II.6 | User account and access-right management | 10 |
| II.7 | Vulnerability management | 10 |
| II.8 | Cybersecurity log management | 9 |
| II.9 | Web browser and e-mail service protection | 8 |
| II.10 | Malware protection | 9 |
| II.11 | Data backup and recovery | 10 |
| II.12 | Network infrastructure management | 9 |
| II.13 | Cybersecurity defensive monitoring (level 4 and above only) | 9 |
| II.14 | Operations, system-administration and cybersecurity personnel | 8 |
| II.15 | Product and service supplier management | 8 |
| II.16 | Secure application development (only where software is developed) | 7 |
| II.17 | Cybersecurity incident response management | 10 |
| II.18 | Cybersecurity inspection management | 7 |
| Provision | What It Requires | Operational Implication |
|---|---|---|
| Article 2(1), Article 4(2) | Ministries, ministerial-level agencies and provincial People's Committees assess their systems in the pilot and report to the standing body. | A State body plans its pilot assessment. A private organisation has no reporting route. |
| Article 2(1) | Any other organisation may study the Index and organise its own assessment. | A self-assessment is elective and stays the organisation's own. |
| Appendix III | Each assessment item is given a Mức from 0 to 3, the highest the system meets. A Mức counts only with an explanation and evidence for the period. | Keep the explanation and evidence for each item you score. |
| Appendix III | An item that does not apply is left out only where the exclusion is explained and evidenced. Otherwise it is recorded at Mức 0. | Record why an item does not apply, with its evidence. |
| Appendix II, Appendix V | Group I is recorded only at Mức 3 or Mức 0, because it measures compliance with the law. | Hold the approved dossier and the deployed plan as evidence. |
| Appendix III, Appendix IV | The Decision gives a per-system and a per-agency calculation, with maturity levels at 1.4, 2.1 and 2.7. | The official result is the standing body's (Article 4(1)). |
| Appendix VII | Group III statistics carry no weight. For III.2 to III.8, a figure may not be lower than the competent authority recorded. | Record each statistic with its components, period and source. |
| Appendix III, Appendix VI (II.15, II.16.1.3) | Where a State body does not run its system itself, it asks the operator to take part in the assessment under its procedures; a shared-infrastructure operator is responsible for assessing the criteria within that infrastructure; a cloud provider's certification against another standard covering an item can count; suppliers are reached through the owner's contracts. | An operator, host or supplier may be asked for evidence, and a shared-infrastructure operator assesses its own part. |
| Article 3(1) | Results are kept confidential, and state-secret content follows the Law on Protection of State Secrets. | Keep classified material in the systems authorised to hold it. In ComplianceOne, record only non-classified details, aggregate counts and references to that evidence. |
| Phase | Timing | Reference |
|---|---|---|
| The Decision takes effect | 12 October 2026, on signature | Article 5 |
| Pilot assessment by ministries, ministerial-level agencies and provincial People's Committees | 2027–2028 | Article 1(1), Article 2 |
| Reports to the standing body | By the deadlines the standing body's guidance sets; no period is stated | Article 4(2) |
| Preliminary review of the pilot | Second quarter of 2028 | Article 1(1) |
| Official application | 2029–2030, only if the Prime Minister so decides | Article 1(2) |
The Decision prescribes no filing form. Appendix II is a criterion table, Appendices III and IV are methods, and Appendices V to VII are assessment catalogues. ComplianceOne carries four internal templates, which its registers read: the assessment catalogue, the assessment period, the Group III statistic and the supplier evidence request. None is an official form, and none is filled on its own: you record on the registers described below.
Add Decision 1964 to your workspace from the sector overlay catalogue. You choose whether to install it for reference or apply it directly, and the choice is the same for every organisation, State bodies included. Reference is preselected for everyone, and the choice is yours. No install mode makes the Index binding on an organisation the Decision does not address. Sector overlays, this one included, are available in the Enterprise package only.
Three registers, under Sector Overlays › Cross-Sector (part of the Enterprise Unlimited package). They take records once you apply the Decision directly. Installed for reference, the criteria, the catalogue and the guidance stay readable and the registers take no record.
Each period exports as CSV, Excel, PDF or Word, in English or Vietnamese, and the first line reads The organisation's own self-assessment against the pilot scale; not an Index result. The file carries the whole period: its people and systems, each item with its evidence, date statements and parties, the statistics with their derived values, and the supplier requests with their replies. A period keeps the catalogue it was opened against, and a closed period accepts no change.
What ComplianceOne does not do. It computes no Index score, maturity level or grade. It performs no State body's assessment and none of the Appendix III and IV score calculations. It submits nothing to the Ministry of Public Security, sends no report to the standing body and is not the standing body's assessment tool. It ranks no one, publishes nothing and certifies nothing.
A self-assessment is only worth the evidence behind it. The Index counts a Mức only when the explanation and the evidence for the period are on file.
Each criterion sits on the framework record with its weight, the systems it applies to and the articles it comes from. Your team reads the scale as the Decision issued it; its annexes may be revised during the pilot.
Every criterion says plainly that it is a self-assessment item, not a duty. A Mức you reach is not presented as an Index grade or as conformity with a standard.
Installing the Decision, and any later change to its install mode, is written to the audit trail. Who chose it, and when, can be shown later.
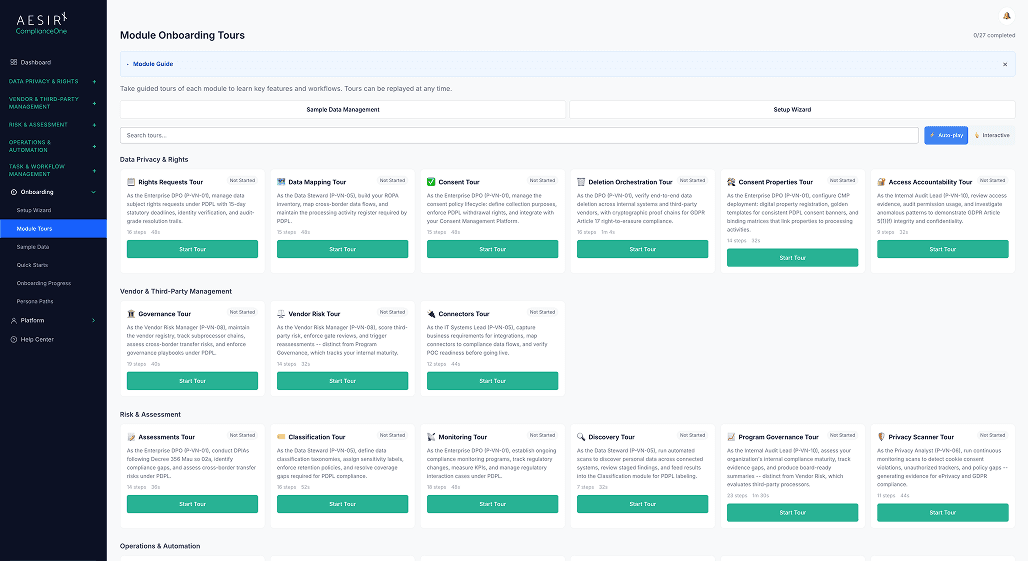
Ready to see how ComplianceOne's command center, guided setup, platform administration, and AI advisor work together in practice? Request a personalized demo with your compliance scenarios.
Ronni K. Gothard Christiansen - Technical Privacy Engineer & CEO
Technical Compliance Expert, 32+ Years Open Source Advocate, X-BoD Open Source Matters Inc.
No. The Decision binds the Ministry of Public Security and the ministries, ministerial-level agencies and provincial People's Committees in the pilot. Any other organisation may use the Index to assess itself, by choice. The Decision says its scales are not a mandatory technical regulation or standard.
Possibly. Where a State body assesses a system you operate, host or supply, it may ask you to take part and to provide evidence for the criteria within your scope; if you operate shared infrastructure the system runs on, you are responsible for assessing the criteria within that infrastructure (Appendix III). That request comes from the system owner, through its procedures and contracts. You have no reporting route to the Ministry of Public Security of your own.
No. The official result is the standing body's. ComplianceOne shows the criteria, the method and the evidence each item needs. It does not compute an Index score, a maturity level or a grade.
No. The standard deployment is not a system authorised to hold State secrets and cannot tell what is classified, so classified State-secret material must not be taken into it, processed, reproduced or exported there. Where the law allows, you can record non-classified details of an assessment, aggregate counts and references to evidence held in a system authorised to hold it. Classified evidence that is not held in ComplianceOne is never treated as non-compliance.
Yes, as its own record. A ministry, ministerial-level agency or provincial People's Committee that applies the overlay directly is assigned the pilot item and can open periods in the pilot role, with its entries and statistics. The assessment, the Appendix III and IV score calculations and the report to the standing body remain the body's own acts. ComplianceOne performs none of them, computes no Index score and sends nothing to the Ministry of Public Security.
Not during the pilot. Index results are confidential. Pilot results are used to refine the Index and are not published or ranked. Only if the Prime Minister decides official application for 2029–2030 would official results of the assessed bodies be published and ranked each year.
No. The duty to determine a system's level and hold an approved dossier, where it exists, comes from the Cybersecurity Law and Decree 331/2026/NĐ-CP. The Index scores that dossier and plan as criteria I.1 and I.2.
No. The Decision states no sanction. Administrative penalties in cybersecurity are set by Decree 330/2026/NĐ-CP, and none is tied to an Index score.

Read the 29 criteria against your own systems and the evidence you already hold.

Talk through which of your systems are at level 3 or above, and which criteria apply to them.


The evolution of Aesir is Aesir +  (the Norse symbol for Necessity)"Needed in order to achieve a particular result"
♥Join the AesirX Privacy Newsletter. Stay Informed. Stay Compliant.