

DPO Radio
Document Review
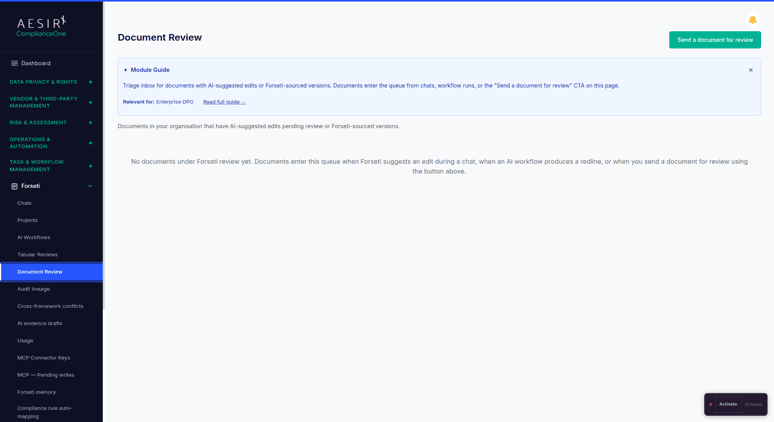
Upload a draft contract, DPA, or policy memo. Forseti proposes redlines as suggested edits. The reviewer accepts or rejects each, building a new version of the document.


A legal counsel reviewing a vendor DPA needs three things in parallel: an authoritative clause library, jurisdiction-aware risk language, and a record of which suggestions were rejected and why. Most "AI contract review" tools provide the first, gesture at the second, and lose the third entirely. The result is a fast first-pass markup that the legal counsel cannot defend in an audit because there is no record of the rejections.
Forseti's document review surface keeps all three intact. Forseti proposes redlines drawn from the clause library, with jurisdiction-aware risk language pinned to PDPL, GDPR, DORA, or NIS2 as relevant. Each redline is a suggested edit the reviewer accepts or rejects. Versions are immutable. Rejections are recorded along with the operator and the time of rejection. When an auditor asks why a clause was not accepted, the answer is in the version history.
The same surface works for contracts, DPAs, vendor agreements, governance documents, and policy memos. The clause library and the risk-language pinning adapt to the document type and the installed regulatory packs.
Per-edit accept or reject with immutable version history
Upload a draft document. Forseti proposes redlines per clause with citation to the relevant framework requirement and risk language. The reviewer walks the redlines, accepts what is right, rejects what is not, and the platform builds an immutable new version with both the accepted edits and the rejected suggestions recorded.
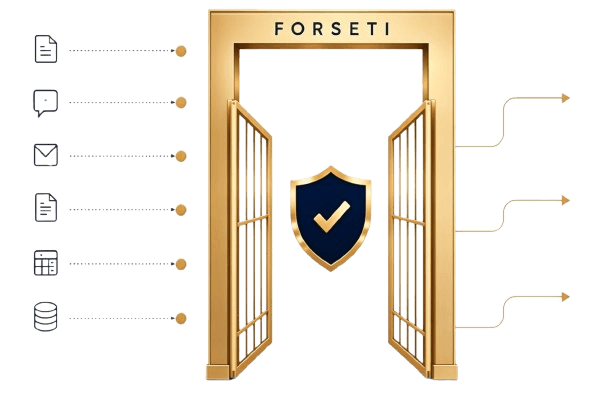
No redline auto-applies. Every accepted edit is an operator action recorded in the version history.
No rejected suggestion is silently dropped. Rejections persist in the version history with operator and time.
No legal conclusion ships without an inline citation. Suggestions that cannot be grounded carry a "no grounding" marker rather than fabricated authority.
No cross-organisation document leakage. Documents are scoped to the customer organisation.

Validate the file and preview Word versions where conversion is configured. Document Search and Tracked Redlines shows coverage and source locations in permitted project documents. Contract Playbooks compares an agreement against versioned negotiating positions and gives the reviewer a finding for each rule.
An authorised reviewer can turn accepted, source-supported findings into tracked changes in a new Word version. Use quote verification to inspect the wording, and Tabular Reviews to compare terms across several documents.
Ready to see a vendor DPA reviewed against GDPR Article 28 in three minutes, with per-clause citations and a clean rejection record? Request a personalised demo.


Ronni K. Gothard Christiansen - Technical Privacy Engineer & CEO
Technical Compliance Expert, 32+ Years Open Source Advocate, X-BoD Open Source Matters Inc.

Pilot Forseti document review against your active contract pipeline. Measure how the rejection record holds up against your audit standard.

Talk to our team about which document types — contracts, DPAs, governance documents, policy memos — to prioritise in the pilot.
Contracts, DPAs, vendor agreements, governance documents, and policy memos. The clause library and the jurisdiction-aware risk-language pinning adapt to the document type and the installed regulatory packs (PDPL, GDPR, DORA, NIS2, ePrivacy national overlays).
Each rejection persists in the document's immutable version history along with the operator who rejected and the time of rejection. The reviewer can add a rejection reason. When an auditor asks why a clause suggestion was not accepted, the record is in the version history.
Yes. Document versions are immutable, but the reviewer can roll forward to a new version that reverts the change. The original accepted edit remains in the version history as an audit record.
Yes. Suggestions are pinned to the relevant framework requirement (e.g. GDPR Article 28 for processor obligations, PDPL Article 31 for the protection measures on biometric and location data, DORA Article 28 for ICT third-party registers). The reviewer sees the citation alongside the suggested wording.
The second review runs against the latest version. The redlines from the second pass are layered on top of the existing version history, so the document carries the full provenance — first-review accepted edits, first-review rejected suggestions, second-review accepted edits, second-review rejected suggestions. Auditors can walk the history end to end.


The evolution of Aesir is Aesir +  (the Norse symbol for Necessity)"Needed in order to achieve a particular result"
♥Join the AesirX Privacy Newsletter. Stay Informed. Stay Compliant.





