DPO Radio
 VIETNAM DATA LAW
Manage data inventory, classification, sharing, transfer governance, evidence, and the instruments that sit beneath Law 60/2024/QH15.

The Vietnam Data Law is the parent framework for broad data governance in Vietnam. It reaches beyond personal data to address digital data assets, their classification, use, sharing, and movement. Organizations need a reliable view of what data they hold, how it is governed, and which records support each decision.
The framework now has four promulgated operational layers. Decree 165/2025/NĐ-CP supplies the general implementing procedures and forms. Decree 169/2025/NĐ-CP adds the data-products and data-services layer. Decision 20/2025/QĐ-TTg provides the official important and core data classification list. Decree 314/2026/NĐ-CP, issued on 8 August 2026 and effective 25 September 2026, governs the operation of data platforms — the venue where data is traded.
Decree 314 is the promulgated form of the instrument previously tracked as the 2026 data-exchange draft. That draft is retained for lineage and its references still resolve, but it no longer states current law, and readiness records keyed to its article numbers need re-checking rather than carrying forward.
This distinction matters in practice. Obligations that are in force need controlled execution and evidence; an instrument that is issued but not yet effective needs dated preparation; a superseded draft needs its evidence preserved and its assumptions re-tested. Blending the three creates unreliable plans and misleading evidence.
ComplianceOne keeps the parent law and each child instrument connected without flattening their legal status. Teams can manage current work, prepare against a dated effective date, and keep the superseded layer readable as history.
Law 60/2024/QH15, covering enterprise data governance, classification, sharing, and transfer controls.
Decree 165/2025/NĐ-CP and Decree 169/2025/NĐ-CP, both active implementing layers.
Decree 314/2026/NĐ-CP on the operation of data platforms, issued 8 August 2026 and effective 25 September 2026.
Decree 326/2026/NĐ-CP on location identification, issued 19 August 2026 and effective 1 September 2026 — a national-database instrument with the Data Law among its legal bases.
Decree 363/2026/NĐ-CP on administrative sanctions in the data field, issued 19 September 2026 and effective 11 November 2026 – distinct from the cybersecurity and personal-data sanctions decree.
Decision 20/2025/QĐ-TTg, the important/core data classification reference.
The 2026 Data Exchanges Draft, promulgated as Decree 314 and retained so historical references and readiness evidence stay addressable.
Data registers, classification decisions, approvals, risk reviews, transaction records, supporting documents, and audit history.
Eleven Decree 165 forms, ten verified Decree 169 forms, and the single Mẫu ĐK01 under Decree 314; Decision 20 remains a list, not a form pack.
In-force obligations, dated preparation for an upcoming instrument, and superseded draft history are each carried separately.
Decree 165 adds the operational layer beneath the Data Law. ComplianceOne supports the decree’s procedures, timelines, risk areas, guidance, and eleven official Forms (Mẫu số) without duplicating the parent law’s role.
Decree 169 adds data-product and data-service governance, including inventories, provenance, quality, update controls, customer or recipient governance, and verified official forms.
Decree 347, issued on 8 September 2026 and in force from 15 September 2026, amends Decree 169 in its first chapter: providers of data analysis and aggregation products or services notify the National Data Centre before operating and report annually on BC01 before 20 December; intermediary licensing is widened to cover analysis and aggregation; the separate business-in-analysis certificate and its forms are abolished; data-exchange operators carry a personnel condition; and certificates issued before commencement remain usable until they expire. Decree 169 stays in force and is read together with it.
Decree 363, issued on 19 September 2026 and effective 11 November 2026, is the Data Law's own administrative-sanctions decree. It sanctions collection and creation, classification, storage, governance, access, sharing, analysis and aggregation, publication, encryption, cross-border transfer of core and important data, data exchanges, intermediaries, the National Data Development Fund and controlled testing. Stated amounts are individual levels and organisations are fined twice, except in five provisions stated for organisations; the individual maximum is 100 million VND, and suspension of an exchange, a database or a certificate can outweigh the fine. It expressly excludes the conduct the cybersecurity and personal-data sanctions decree governs, so it is a separate track from Decree 330 and is never added to it.
Decision 20 supports classification screening and escalation. It is an official list and reference artifact, not a prescribed form set.
Decree 314 governs the operation of data platforms: the National Data Platform and other platforms, information-system security level 3, participant and data eligibility, listing review, controlled testing, electronic contracting, transaction traceability, pricing and revenue sharing, risk management and dispute support. It carries one official form, Mẫu ĐK01, and takes effect on 25 September 2026.
Decree 326 establishes location identification: one stable 12-digit code per identified location, assigned by the state's Location Identification Database under the Ministry of Public Security, across 71 annex object classes. It is a Government decree with the Data Law and the Personal Data Protection Law among its legal bases, carried in this family for its national-database and data-exploitation machinery. Location owners carry no filing duty; the substantive duties fall on data exploiters and connected organizations. It takes effect on 1 September 2026, with no fines and no official forms.
The draft that preceded Decree 314. It is retained so historical references resolve and readiness evidence built under it stays addressable, and it no longer states current law.
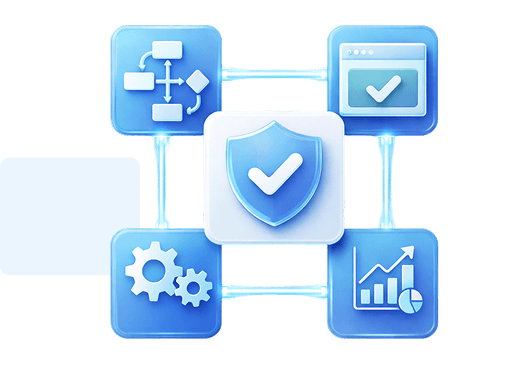
ComplianceOne connects data discovery, mapping, and classification records so teams can maintain a governed inventory rather than a collection of disconnected spreadsheets. Review and approval records show how classifications and handling decisions were made.
For Decree 165, the platform brings current forms, procedures, deadlines, guidance, and risk records into the same controlled workspace. Teams can assign owners, prepare supporting evidence, review form content, and preserve a complete history of changes and approvals.
For Decree 169 and Decision 20, teams can connect product and service inventories, provenance, quality, update controls, and important/core data screening to accountable decisions and supporting evidence.
For Decree 314, the platform carries the instrument with its effective date, so it reads as upcoming until 25 September 2026 and as active after it. Its timed obligations – the 24-hour suspension, the 5-working-day verification, the support windows and the ten-year traceability retention – are held as deadlines a programme can be measured against, and the preparation templates authored during the draft period were re-pointed to it rather than duplicated.
For Decree 363, every fine area is carried with its attribution rule, suspension exposure and the obligation it sanctions, and it reads as upcoming until 11 November 2026. Penalty Readiness computes the range for the party that applies once exposure inputs are recorded; which enforcement track an exposure sits on remains a person's determination.
Evidence packs and audit history provide a reviewable record of completed work. Where Data Law activity overlaps personal data protection or cybersecurity, the same underlying evidence can be linked to the relevant obligation without losing its original context.
 Data Mapping
Maintains data inventories, system relationships, and data-flow records.
Explore Data Mapping Data Classification
Records classification decisions, review status, and linked handling expectations.
Explore Data Classification Program Governance
Assigns ownership, reviews, recurring work, and regulatory-change actions.
Explore Program Governance Compliance Forms
Supports official forms and controlled supporting documentation.
Explore Compliance Forms
 The parent law and its implementing instruments are treated as one undifferentiated checklist.
 Parent, active, upcoming, and superseded instruments retain their correct status and relationship.A superseded draft and the decree that promulgated it are cited interchangeably.In-force Decree 165 work, dated Decree 314 preparation, and superseded draft history stay distinct.Data inventories and classification decisions become stale or lose ownership.Data records, decisions, owners, and supporting evidence remain connected.Official forms are prepared separately from the evidence that supports them.Form preparation includes review gates and linked evidence.Review history is reconstructed only when an inspection or request arrives.Audit history is available as work progresses, not assembled retrospectively.

ComplianceOne supports the active Decree 165 layer with its official forms and operational records while preserving the Data Law as the parent framework.

Decree 314 requirements are managed through structured records, deadlines, evidence, and review controls while retaining their relationship to the wider Data Law framework.

Shared evidence and audit history help organizations manage overlaps with personal data protection, cybersecurity, and other Vietnam obligations.
See how ComplianceOne structures current Data Law work and draft-instrument readiness without blurring their status.

Ronni K. Gothard Christiansen - Technical Privacy Engineer & CEO
Technical Compliance Expert, 32+ Years Open Source Advocate, X-BoD Open Source Matters Inc.
The Data Law is the parent framework. Decree 165 is its active implementing decree, adding procedures, timelines, guidance, risk records, and eleven official Mẫu số forms. ComplianceOne keeps the two connected while preserving their different legal roles.
No. It was promulgated on 8 August 2026 as Decree 314/2026/NĐ-CP and takes effect on 25 September 2026. The draft is retained for lineage so historical references resolve, and readiness records keyed to its article numbers should be re-checked against the signed text rather than carried forward.
The platform connects official form preparation to assigned work, supporting evidence, review, approval, and audit history. This helps teams prepare complete records without separating the form from the operational proof behind it.
ComplianceOne includes all 11 Forms (Mẫu số) templates defined by Decree 165/2025/ND-CP (01a through 07b), covering data inventory registers, classification records, governance documentation, and attestation reports. Templates are structured to match MIC-prescribed formats and are available in both Vietnamese and English.
Yes. Data inventories, classification records, transfer documentation, and approvals can be linked to related personal data protection or cybersecurity work while retaining their source and review history.
No. ComplianceOne structures compliance work, evidence, ownership, and review. Organizations remain responsible for legal interpretation and approval of their submissions.
Program Governance can manage recurring governance reviews, assign work to responsible owners, track completion, consolidate inputs, and preserve contributions with timestamps and contributor history.
The Data Discovery module automates identification of data assets across connected systems. Discovered assets are routed to the Data Classification module where they are classified by sensitivity and importance. Classification assignments are reviewed by data owners, and each classification level is linked to operational handling rules, including access control, retention, and deletion.
Yes. Data governance can involve responsibilities across multiple departments. ComplianceOne routes governance tasks to responsible department owners, tracks each department's contributions, and consolidates inputs into unified documentation. Contributor lineage is preserved in the audit trail, showing who contributed what and when.

Test Decree 165 evidence workflows and draft data-exchange readiness with your team.

Review your Data Law instrument stack, evidence needs, and current operating model.

The evolution of Aesir is Aesir +  (the Norse symbol for Necessity)"Needed in order to achieve a particular result"
♥Join the AesirX Privacy Newsletter. Stay Informed. Stay Compliant.
 Data Discovery
 Audit Trail