DPO Radio
Auditor's Eye Persona
Give your internal audit lead an AI voice for walkthroughs, control evidence sufficiency and privilege-creep detection. It works over the frameworks your organisation has installed, your assessments and the Audit Lineage trail.


The Auditor's Eye takes on the recurring work of an internal audit lead who also supports external regulatory inspection:
That work needs fluency in ISO 27001 and SOC 2, knowledge of your evidence library, and forensic discipline that holds up to external scrutiny.
The persona is tuned for exactly that. It reaches first for the audit workflows (audit walkthrough generator, privilege creep detection, control mapping and the Audit Lineage view) and for forensic queries against the audit trail.
The Auditor's Eye is the third-line voice, with the same citation rules as every other persona. Your audit lead stays in charge of every output:
The persona's instructions centre on ISO 27001 and SOC 2 audit work, but no framework text is loaded into it in advance. Each conversation tells it which frameworks your organisation has installed, and it may cite a framework only when its regulatory search returned that text in the same turn. Assessments, evidence and other audit records are read on demand through its search tools, within the permissions of the person asking.
The persona reaches first for the audit workflows: audit walkthrough generator, privilege creep detection, control mapping (framework requirements to your control library) and maturity assessment gap walkthrough. The Forseti Audit Lineage view is one click away from any record the AI has touched.
Walk into the kickoff with a script for every control in scope. Starting from a planned audit, the generator drafts four fields per control:
The audit lead reviews and adapts the set, then exports it as a DOCX.
Find access that has grown beyond policy. The scan compares role assignments with the documented access policy and tags each finding by severity (low, medium, high, critical). Each finding proposes a written remediation naming the permissions of concern. The auditor routes each one to its owner; nothing is ever revoked automatically.
See where evidence falls short of what a control claims. The persona walks the evidence chain against the control assertion and lists the gaps, each with a citation to the control requirement and a suggested next step.
Ask questions that span records, such as "show me every AI-initiated draft on this DPIA over the last quarter, who approved each, and the resulting record state". The Audit Lineage view assembles the answer.
Questions about contract redlines or vendor risk acceptance are redirected to the Legal Counsel or Risk Analyst persona. Questions outside audit work altogether get the standard off-topic refusal.


 Walkthrough scripts are reconstructed manually for each audit cycle.
 The persona works over the frameworks your organisation has installed and reads audit records on demand.Privilege-creep reviews are bespoke per analyst, with no consistent severity scoring.The audit workflows are one click away from any audit record.Evidence sufficiency reviews live in spreadsheets that drift from the underlying control assertions.Privilege-creep findings carry consistent severity tags and suggested remediation routes.Forensic queries against the audit trail require manual cross-referencing across systems.Forensic queries run against the Audit Lineage view with full chain-of-custody.

Every audit conclusion comes with an inline citation to the control requirement. Walkthrough scripts, sufficiency findings and privilege-creep results all cite the framework.

Findings are drafts for the audit lead, who routes each one to its owner. The persona takes no remediation action itself, and each routing decision is recorded in the audit trail.

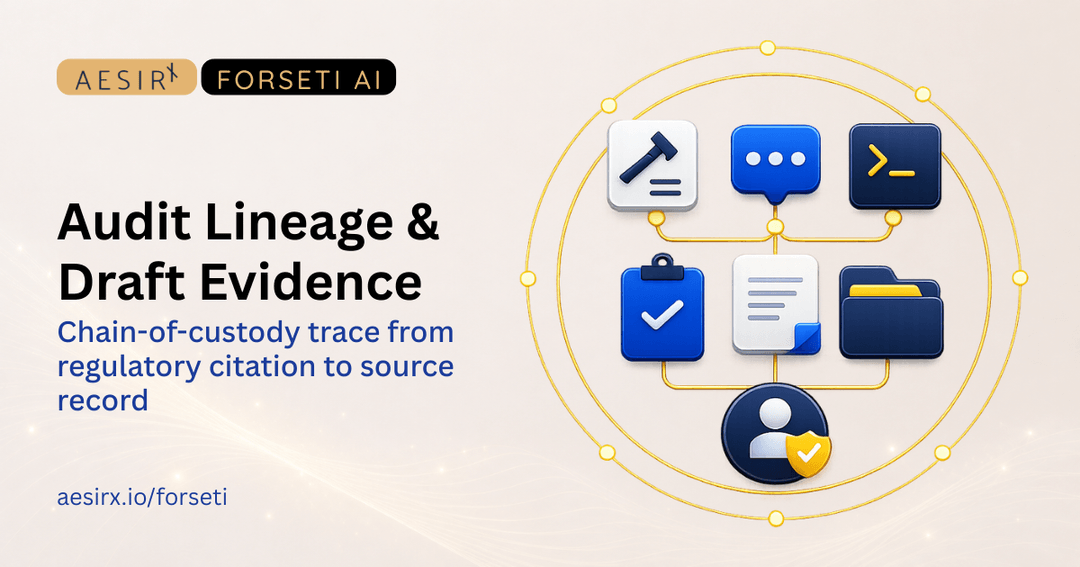
For inspection readiness, use the Audit Lineage view. Every record the AI has touched traces back through its chats, tool calls, workflow runs, drafts, approvals and downstream changes.

Use the Auditor's Eye playbooks in English or Vietnamese to prepare a sample, challenge a Forseti draft or follow a risk to its controls. Open Internal Audit Workflows or Evidence Workflows on the relevant record.
See a walkthrough script generated for an ISO 27001 Annex A control and a privilege-creep scan run against your access governance, in five minutes. Request a personalised demo.


Ronni K. Gothard Christiansen - Technical Privacy Engineer & CEO
Technical Compliance Expert, 32+ Years Open Source Advocate, X-BoD Open Source Matters Inc.

Run the audit walkthrough generator and the privilege-creep scan through the Auditor's Eye for 30 days on your ISO 27001 and SOC 2 control sets.

Talk to our team about how the Auditor's Eye fits into your internal audit cadence and your external inspection-readiness posture.
Audit walkthrough generation, privilege creep detection, control evidence sufficiency review, compliance rule auto-mapping (framework requirements to your control library), and forensic queries against the Audit Lineage view. It reaches first for the audit workflows and the audit trail.
The ones your organisation has installed. Its instructions centre on ISO 27001 and SOC 2, but no pack is loaded into it in advance: each conversation tells it which frameworks are installed, and it cites a framework — ISO 27001, SOC 2 or any other you have installed — only when its regulatory search returned that text in the same turn.
No. Findings are drafts, and the audit lead reviews each one. The lead routes it to its owner using the written remediation the finding carries, and the routing decision is recorded in the audit trail.
It compares role assignments with the documented access policy and tags each finding by severity (low, medium, high, critical). Each finding carries a suggested remediation. The audit lead reviews each finding and routes it to its owner.
No. The Auditor's Eye prompt is identical on Light, Standard and Enterprise, and no tier lets an organisation override it. You can review it on request. Each conversation picks up your own context: the user's locale and role, your tier, and the frameworks added to your workspace.


The evolution of Aesir is Aesir +  (the Norse symbol for Necessity)"Needed in order to achieve a particular result"
♥Join the AesirX Privacy Newsletter. Stay Informed. Stay Compliant.