

DPO Radio
ACTIVE
 Decree 327/2026/NĐ-CP – Violating-Information Handling
The procedural decree for handling information and acts that infringe national security or social order in cyberspace, issued and effective 19 August 2026.
Meet removal directions, data-provision windows and the emergency standby duty on the decree's own clocks.

If you run an information system or provide online services in Vietnam, Decree 327/2026/NĐ-CP sets how fast you must act when the authorities direct you. It applies in full from 19 August 2026, the day it was issued. There is no transitional period.
The Government issued the decree to detail Article 14 of Cybersecurity Law 116/2025/QH15. It has 16 articles in five chapters, and the Ministry of Public Security is the lead authority.
The decree covers five things:
Three clocks drive compliance:
| Clock | Standard | Emergency |
| Report a serious cyberattack | 24 hours | — |
| Provide requested data | 24 hours | 3 hours |
| Remove violating information | 24 hours | 6 hours |
The removal and data-provision clocks apply to the people who posted the information, not only to providers. If removal is late, the specialized force may access and delete the information itself.
Decree 327 turns the Cybersecurity Law's protective measures into a working procedure for violating information and acts. Cybersecurity Law 116/2025/QH15 is the parent law.
Two related decrees draw its boundaries:
| Provision | What It Establishes | Operational Implication |
|---|---|---|
| Article 5 | Preventive duties: user identification and fake-account blocking, retention and state-secret compliance, cooperation and platform interoperability, immediate response to warnings, and the 24-hour serious-attack report | These duties apply all the time, not only when a request arrives |
| Article 5(1)(h) | Payment intermediaries and digital-asset providers face liability if they continue serving accounts on the specialized force's warning list | It does not require automatic suspension. Providers need warning-list controls and a legally reviewed response |
| Article 6 | The managerial and technical control catalogue over content and accounts, plus electronic-evidence preservation | Authorities can inspect your controls and evidence handling |
| Article 7 | Seven handling-measure families — blocking, suspension, domain, content-control and account measures among them — each ending in an open catch-all | Your intake process must handle directions that fit none of the listed measures |
| Article 7(2)(h) | Removal of unlawful or false information within 24 hours, 6 in emergencies; on failure the force may itself access and delete | Missing the deadline has a stated consequence |
| Article 7(11) | Information and electronic data provided within 24 hours of a request, 3 in emergencies | You need to be able to extract and approve data out of hours |
| Article 10(7)–(9) | Posters remove the content, report the removal result to the requesting force, disable sharing/copying/distribution, prevent reposting, remove related links/data, and meet the stated data-provision clocks | Organizations need removal, anti-spread and result-reporting evidence, not only a deleted post |
| Article 13(1) | On detecting an emergency, immediately mitigate and notify; preserve system state, data and evidence; and immediately comply with coordination, technical and blocking requests | Emergency records must show the first action, notice, preservation and execution sequence |
| Article 14(2) | A designated coordination focal point on 24/24-hour standby for emergency requests, execution and result reporting | Someone must be available at all times, and you must be able to prove it |
| Article 14(3)–(4) | Standardized coordination forms and channels are delegated to the Ministry of Public Security, and to the Ministry of National Defence for military systems | Watch for ministerial guidance; the decree itself numbers no forms |
| Obligation | Timeline | Reference |
|---|---|---|
| Decree takes effect | 19 August 2026, no transitional provisions | Article 15 |
| Report a qualifying cyberattack | 24 hours from detection | Article 5(1)(g) |
| Provide information and electronic data | 24 hours from the request | Article 7(11)(a) |
| Provide data in emergency situations | 3 hours | Article 7(11)(b) |
| Remove unlawful or false information | 24 hours from the request | Article 7(2)(h) |
| Remove in emergencies | 6 hours | Article 7(2)(h) |
| Poster removes content, copies, links and re-shares | 24 hours; 6 in emergencies | Article 10(7) |
| Poster provides related information and data | 24 hours; 3 in emergencies | Article 10(9) |
| Emergency mitigation, notice, preservation and coordination | Immediately upon detection | Article 13(1) |
| Emergency coordination standby | Continuous, 24/24 hours | Article 14(2) |
There are no official forms to file under this decree yet. The Ministry of Public Security will set the standard coordination forms, and how requests are sent, received, authenticated and answered. The Ministry of National Defence does the same for military information systems. Any template ComplianceOne supplies for this decree is an internal preparation template and is labelled as one.
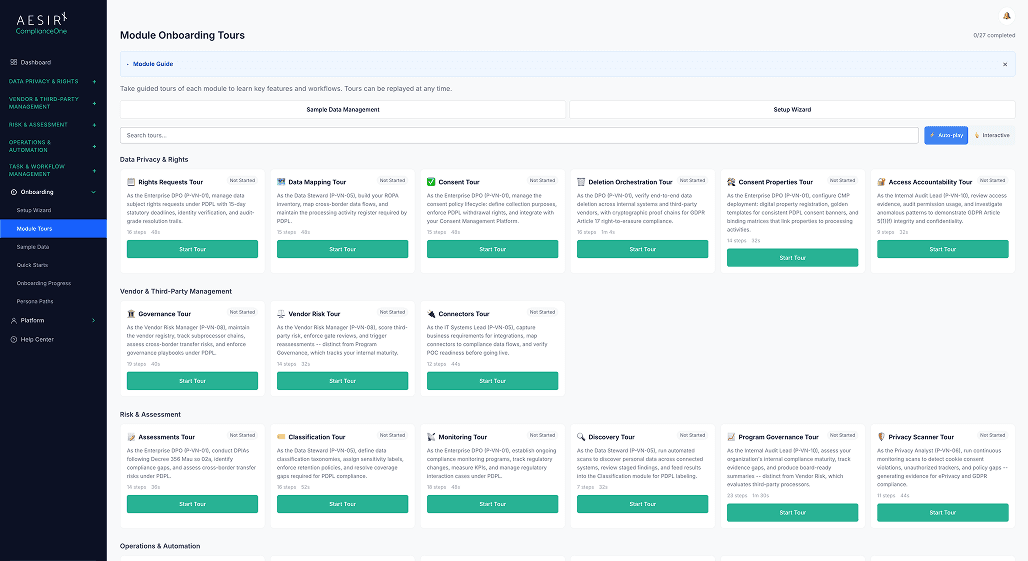
Once Decree 327 is added to your workspace, ComplianceOne lists its duties, handling measures and clocks, each citing the article it comes from. The open "other measures" clauses are shown as open, not narrowed to a fixed list.
You can record each direction or request with its verified receipt time, scope, owner, execution steps and proof of completion. That is the evidence that shows a 6-hour clock was met rather than assumed.
Evidence preservation runs as chain-of-custody work: what was captured, by whom and when, and proof that it reached the authority intact.
Provider duties and poster duties sit side by side. One organization can be both, and the two roles have similar but separate clocks.
The clocks start when a direction arrives, not when your team notices it. ComplianceOne records a verified receipt time, because the difference between hour one and hour five is the whole compliance question.
The consequence goes in the record too. If removal is late, the force may act directly, so your file should show why the window was met.
A direction that fits none of the listed measures still gets intake, execution and evidence. It does not fall between categories.
When one event makes you both provider and poster, each request is answered in the role it names, against the right clock.
 Incident Response
Coordinates direction execution, escalation and the 24-hour attack report on one evidence chain.
Explore Incident Response Incident Operations
Keeps warnings, responses and authority interactions connected to the case.
Explore Incident Operations Program Governance
Assigns the standing duties — verification, controls, standby — to accountable owners
Explore Program Governance Monitoring Programs
Tracks recurring control reviews, fake-account screening and vulnerability remediation.
Explore Monitoring ProgramsOrganizations operating under Decree 327 should confirm:
See how ComplianceOne records directions, runs the removal and data clocks, and keeps the custody evidence.

Ronni K. Gothard Christiansen - Technical Privacy Engineer & CEO
Technical Compliance Expert, 32+ Years Open Source Advocate, X-BoD Open Source Matters Inc.
Yes. Decree 327/2026/NĐ-CP was issued on 19 August 2026 and took effect the same day under Article 15. The text sets no transitional provisions or grace periods.
Information-system owners and a broad class of service providers carry the preventive and execution duties. People who posted the information have their own removal and data-provision duties. Payment intermediaries and digital-asset providers are also covered: under Article 5(1)(h), continuing to serve an account on the specialized force's warning list creates liability. That clause does not require automatic suspension.
Removal of unlawful or false information is due within 24 hours of the specialized force's request, or 6 hours in emergencies. After that, the force may access and delete the content itself. Information and electronic data are due within 24 hours, or 3 in emergencies. Posters have the same clocks for their own content and data.
No. Decree 327 sets duties and measures but no fines. The fine schedules are in Decree 330/2026/NĐ-CP. Any amount quoted from it needs the rule on whether it applies to an individual or an organization.
Decree 328 governs fake and false information specifically and has applied since 5 October 2026. Before that date, directions and clocks for that content came under Decree 327, which also covers the wider class of violating information. Both decrees sit under the same Cybersecurity Law.

Test direction intake, clock evidence, custody records and the standby duty against the signed decree.

Review your provider and poster exposure, your out-of-hours capability, and your coordination readiness.


The evolution of Aesir is Aesir +  (the Norse symbol for Necessity)"Needed in order to achieve a particular result"
♥Join the AesirX Privacy Newsletter. Stay Informed. Stay Compliant.
 Audit Trail






