DPO Radio
ACTIVE
 Decree 94/2025/NĐ-CP Controlled Testing in Banking
Decree 94/2025/NĐ-CP of the Government sets the controlled testing mechanism in banking. It was issued on 29 April 2025 and took effect on 1 July 2025.
The mechanism covers three kinds of Fintech solution: credit scoring, data sharing through an open application programming interface, and peer-to-peer lending. Credit institutions and foreign bank branches may take part in credit scoring and open-API solutions. Peer-to-peer lending is open to Fintech companies only: Article 2 Clause 1 excludes it for credit institutions and foreign bank branches.
Each solution is assessed against written criteria. A Fintech company files on one dossier track, and a Fintech company offering peer-to-peer lending files on a second. The State Bank decides every application. The testing period is up to two years.
The 2025 text is the base. Decree 382/2026/NĐ-CP, in force on 6 October 2026, changes several periods and filing rules. Its Article 14 Clause 1 keeps the 2025 procedure for a dossier whose receipt the State Bank confirmed in writing before 6 October 2026.
The State Bank's written confirmation of a complete set is the date that separates the two appraisal regimes. Check the confirmation date on your own file before applying either row.
An extension request is filed at least 90 days before the testing period ends, and each extension runs at most one year, twice at most. The State Bank may stop testing on the grounds Article 19 lists. After a stop the organisation carries out its exit plan, tells its customers at least 30 days before the stop for grounds a and b (at once for grounds c, d, đ, e, g and h), settles their rights within six months and reports the outcome.
A completion certificate is issued on one of two grounds in Article 21 Clause 1. Under (a), an official legal regulation for the Fintech solution has been completed and is in force: the organisation is granted the certificate and then follows the law in force at the time of completion. Under (b), testing has been assessed as not violating current law and the solution is not a conditional business activity. The application is filed on Form No. 11 (Mẫu số 11) with the Appendix V report (Article 21 Clause 2).
The text does not define the terms of the 24-hour incident clock (Article 15 Clause 7): "sự cố gây gián đoạn hoạt động" and "rủi ro nghiêm trọng" are undefined in Article 3. An organisation should take its own reading with counsel.
Built for Dates and Reports You Can Check
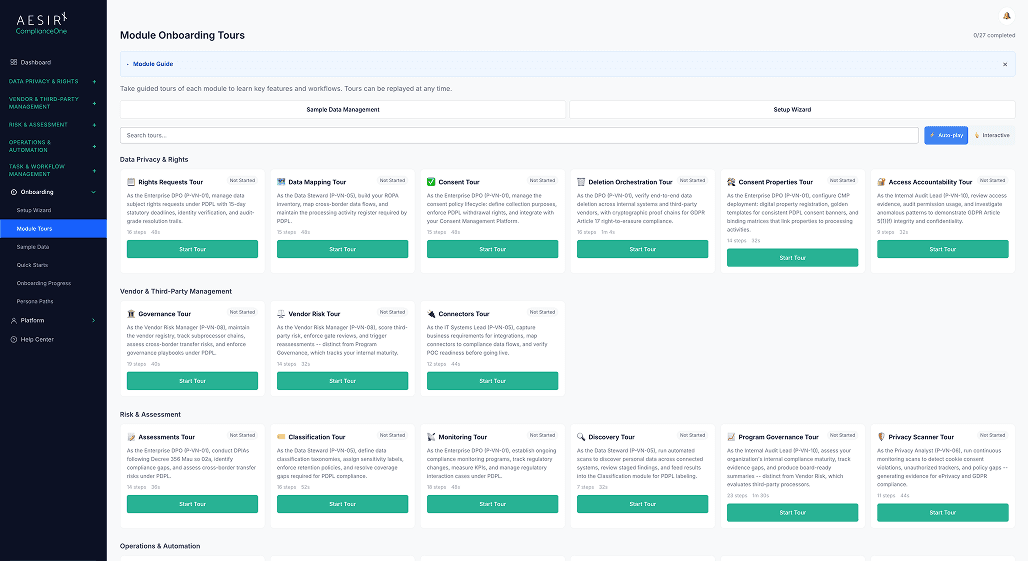
A reporting clock is only as good as its record. ComplianceOne keeps each application's dates, its reports and the evidence each rests on in one place.
A date that has not been entered is shown as missing. The check lists it, so the gap is closed by the organisation before the State Bank reads the file.
Each change to a record is written to an audit log with a timestamp, so who prepared a report, and when it changed, can be shown to a reviewer.
The State Bank decides every application. ComplianceOne holds the dates and the evidence, and does not replace the appraisal or the State Bank's decision.
See how ComplianceOne keeps your controlled-testing applications, reporting deadlines, incident records and supporting evidence in one place.
Ronni K. Gothard Christiansen - Technical Privacy Engineer & CEO
Technical Compliance Expert, 32+ Years Open Source Advocate, X-BoD Open Source Matters Inc.

Test your reporting deadlines, incident records and evidence under Decree 94.

Review your filing requirements, reporting duties and key deadlines.

The evolution of Aesir is Aesir +  (the Norse symbol for Necessity)"Needed in order to achieve a particular result"
♥Join the AesirX Privacy Newsletter. Stay Informed. Stay Compliant.