DPO Radio
UPCOMING
 Law 23/2026/QH16 Crypto-Asset Anti-Money-Laundering Amendments
Licensed crypto-asset service providers already have AML duties under Resolution 05/2025/NQ-CP Article 15(2)(b), effective since 9 September 2025. Law 23 adds express reporting-entity coverage and crypto-asset suspicious indicators from 1 December 2026; it does not start the existing AML duty. ComplianceOne keeps the governance and evidence records behind that duty in two registers you can use today: your own detection rules, your cases and your reporting decisions.
Law 23/2026/QH16 was passed by the National Assembly on 24 August 2026 and takes effect on 1 December 2026. It amends three laws at once: the State Bank Law, the Anti-Money Laundering Law 14/2022/QH15 and the Credit Institutions Law. The anti-money-laundering amendments are the ones crypto-asset and payments teams need to act on.
What changes for you:
Who is not reached. Using blockchain technology does not make you a reporting entity. The Law reaches a financial institution licensed to provide crypto-asset services, not the people and businesses who use them.
The implementation plan, Decision 1842/QĐ-TTg of 25 September 2026, assigns tasks to the State Bank, the Ministry of Finance, other ministries and the provinces. It places no duty on a private organisation and does not change the 1 December 2026 date.
Law 23 amends the Anti-Money Laundering Law of 2022. It does not replace it. You work from both texts: Law 14/2022 for the regime, and Law 23 for what changes from 1 December 2026. The timing rules for reports, the five-year retention periods, internal rules, risk assessment and the postponement and freezing measures of Law 14/2022 are unchanged. Resolution 05/2025/NQ-CP Article 15(2)(b) already applies financial-institution AML measures to crypto-asset service providers; some AML duties remain specific to a role, product or sector. Continue those current duties while preparing for the amendments.
The banking, fintech and payments overlay already carries the Anti-Money Laundering Law of 2022 and the due-diligence evidence built on it. Law 23 sits beneath that overlay as an amendment.
Decree 284/2026/NĐ-CP is the separate penalty decree for the crypto-asset market pilot. Its Article 13 sanctions anti-money-laundering failures by market participants. Law 23 states no fine of its own. The two are cross-referenced in ComplianceOne and kept apart, so a duty and its sanction each keep their own source.
| Provision | What It Requires | What You Need |
|---|---|---|
| Article 2(2), adding Article 4(1)(n) to the AML Law | Crypto-asset services join the reporting-entity list. The reporting entity is a financial institution licensed to provide them | A dated scope record: whether you hold the licence, and which of your services it covers |
| Article 2(8), replacing AML Law Article 26 | Report to the State Bank where there are reasonable grounds to suspect the asset is proceeds of crime. Reasonable grounds are determined by analysing customer and transaction information, including the statutory indicators and other indicators you identify; since the duty to report is yours, that analysis is yours. Indicators you identify beyond the statutory list are notified to the State Bank | A case record for each investigation, and your own indicators recorded on the coverage record with the date each was notified |
| Article 2(9), adding AML Law Article 33a | Fifteen crypto-asset suspicious indicators. None is itself a duty to report, and none states a numeric threshold | A record mapping each indicator to your own detection rule, owner and threshold |
| Article 2(3), amending AML Law Article 9(2)(c) | Customer due diligence is triggered by suspicion of the customer, the transaction or a related party, including a transaction not completed | Due-diligence records that show the trigger, including attempts that did not complete |
| Article 2(1), (4) and (7), amending AML Law Articles 3, 10 and 22 | The beneficial owner is now one or more individuals who directly or indirectly hold ultimate ownership or ultimate effective control over the customer, including a legal arrangement, or the individual on whose behalf the customer transacts. The former definition was an individual who actually owns an asset and has the power to direct the customer to transact in it for them, or an individual who has the power to direct a legal entity or a legal arrangement. The reach is wider: ultimate ownership of the customer is enough on its own, direct and indirect holdings are named, and the on-whose-behalf limb no longer requires owning the asset and having the power to direct. "Ultimate" may not reach an individual who has the power to direct a legal-entity customer without being its ultimate owner or controller; whether you keep recording that person is your documented reading. A trustee's duty to hold identity data on every party, kept at least 05 years after it stops acting as before, now extends to parties in equivalent roles and adds basic data on the arrangement's agents and service providers | A beneficial-owner and legal-arrangement record for each relevant customer, stating the basis on which each person is recorded |
| Article 2(5), amending AML Law Article 12(1) | The documents accepted for verification, including the identity card and electronic identity card for an individual customer, for an organisation customer, its electronic identification account, and other reliable sources you must judge | Verification evidence naming the document or source relied on, and who accepted it |
| Article 2(6), amending AML Law Article 19(1) | Policies to identify and assess money-laundering risk, issued and applied before a new product or service is offered, or an existing one applies innovative technology. The Law requires no approval and states no lead time | A dated risk assessment recorded before the product is offered; any approval step and its timing are your own control |
| Article 2(10), amending AML Law Article 38(1) | Keep all customer files and all transactions, including CDD data, AML analysis and assessment results, and the reports you made | Case files and analysis kept with the transaction record, on the unchanged five-year periods |
| Article 2(11), adding AML Law Article 39(3)–(4) | A person who reports honestly is not liable for reporting, and reporters are protected as whistleblowers are | Reporting decisions recorded with the person who made them |
| Article 2(13), amending AML Law Article 51 | The Ministry of Finance leads AML measures for crypto-assets and inspects crypto-asset reporting entities when the Government assigns it | Evidence you can produce to the Ministry of Finance as well as to the State Bank |
| Obligation | Timeline | Reference |
|---|---|---|
| Law takes effect | 1 December 2026 | Law 23 Article 4(1) |
| Suspicious-transaction report | 3 working days from the transaction, or 1 working day from detection. The Law joins the two with "or" and does not say which governs. Each case in the Suspicious-Activity Cases register shows both dates, computed from the dates your team recorded, and marks neither as the one that governs | AML Law Article 37, unchanged |
| Suspicious transaction requested by a customer that shows signs related to crime | 24 hours, to the competent authority and the State Bank. This period applies only to that transaction and runs from the time you record as detection of it as crime-linked | AML Law Article 37(3), unchanged |
| Large-value and electronic-transfer reports | 1 working day electronically, 2 on paper | AML Law Article 37, unchanged |
| Record retention | 05 years from the end of the transaction, account closure or report date (reports: from the transaction date) | AML Law Article 38(2), unchanged |
| Legal-arrangement data held by a trustee or a party in an equivalent role | At least 05 years after it stops acting, the period the former Article 22 already set | AML Law Article 22, as replaced |
| Implementation plan milestones | Review of related regulations completed in November 2026; ministers, heads of ministry-level agencies and chairs of provincial People's Committees report their results to the State Bank before 1 April 2027; the State Bank reports to the Prime Minister before 1 May 2027 | Decision 1842/QĐ-TTg |
Law 23 also amends the State Bank Law. Four of those changes bind organisations rather than the State Bank itself:
| Provision | What It Requires | Who It Reaches |
|---|---|---|
| Article 1(3), adding State Bank Law Article 31a | No transaction, payment, listing, advertisement, quotation, pricing or contract price in foreign exchange on Vietnamese territory, except as a law, a National Assembly resolution or the Governor permits. From 1 December 2026, it moves the Article 22 restriction into the State Bank Law. Law 23 Article 4(2) repeals only Article 22 and Article 34(2) of the Foreign Exchange Ordinance; Article 22 continues to apply until then | Every organisation and individual in Vietnam. The Law does not decide whether a given crypto-asset is foreign exchange |
| Article 1(4), amending State Bank Law Article 35 | Supply information for the balance of payments and, newly, the international investment position. A Government decree will say who supplies what, when and how | Organisations the forthcoming decree designates. It is due to the Government before 1 November 2026 |
| Article 1(9), replacing State Bank Law Article 57 | Supply accurate information on request, report and explain on State Bank recommendations and risk warnings, and implement them | Credit institutions and other banking-supervision subjects |
| Article 1(10), amending State Bank Law Article 59 | Where the State Bank sets a different prudential ratio, build and follow a roadmap back to the prescribed level | Credit institutions that receive such a decision |
These appear as requirements in the Law 23 framework alongside the anti-money-laundering duties, so a bank sees them in one place.
The indicators are inputs to your determination, not the determination. Article 26(1) says reasonable grounds are determined by analysing customer and transaction information, "including" these signs, and puts the duty to report on you, so that analysis is yours. Matching an indicator is not by itself a reason to report.
| # | Indicator, in summary |
|---|---|
| 1 | Splitting transactions below the due-diligence or reporting threshold, or many large transactions in a short time with no clear purpose |
| 2 | Activity out of line with the customer's profile: rapid deposit–trade–withdraw after onboarding, a large first deposit right after the crypto-asset account is opened, or a long-dormant account transacting large values or at unusual frequency |
| 3 | Moving assets at once to several providers in jurisdictions on the list the FATF publishes to combat money laundering, terrorist financing and proliferation financing, or in jurisdictions that have issued no AML/CFT/CPF framework, or an incomplete one, for crypto-assets and crypto-asset service providers and are on the list the FATF publishes concerning crypto-assets, with no reasonable link to the customer's residence or place of business |
| 4 | Converting into many assets, or into fiat at a loss or unusually high fees, with no reasonable purpose |
| 5 | Many unrelated accounts or wallet addresses paying one address, or one account paying many addresses in equal amounts in quick succession |
| 6 | Anonymity-enhanced assets, mixing services, or repeated conversion that breaks traceability |
| 7 | Wallet addresses or providers a competent authority has identified or warned about |
| 8 | Anonymising tools, or several identities apparently operated from one device or IP address |
| 9 | Refusing or delaying due-diligence documents, apparently forged documents, or unexplained purpose or source |
| 10 | A wallet address in public sources linked to illegal activity, or history through high-risk cross-chain bridges |
| 11 | Signs of a nominee, a money mule or a fraud victim |
| 12 | Assets sourced mainly from opaque or apparently fraudulent initial offerings, mixers or providers without AML controls |
| 13 | Dealing with a provider whose valid legal status cannot be established, including one operating in a jurisdiction that has no legal framework on crypto-assets according to the list the FATF publishes concerning crypto-assets, one not on its host regulator's licensed list, or one warned, suspended or with its licence revoked |
| 14 | Suspicious memo text, frequent changes to identity or authentication data, inconsistent IP data, or several accounts opened from one IP address |
| 15 | Transacting through a provider headquartered or operating in a jurisdiction on the list the FATF publishes to combat money laundering, terrorist financing and proliferation financing, or in a jurisdiction that has issued no AML/CFT/CPF framework, or an incomplete one, for crypto-assets and crypto-asset service providers and is on the list the FATF publishes concerning crypto-assets |
The Law names no FATF jurisdiction and sets no number for "large value", "short time" or "long dormancy". Your thresholds are yours to set and record.
Law 23 prescribes no report form or channel for crypto-asset suspicious transactions. The amended Article 26(4) leaves the reporting regime to the Governor of the State Bank. No Governor's regulation under the amended Article 26 (Law 23 Article 2(8)) had been published when checked on 18 October 2026. The State Bank's existing reporting rules under Law 14/2022 are not packaged or described here, so the report channel is free text and no form is modelled. Decision 1842/QĐ-TTg assigns the Law's detailing texts to the list in Decision 1772/QĐ-TTg, which names a decree amending Decree 19/2023/NĐ-CP and a State Bank circular amending Circular 27/2025/TT-NHNN for Law 23. Neither had been issued when checked, neither is specific to crypto-assets, and nothing in ComplianceOne states what they will contain.
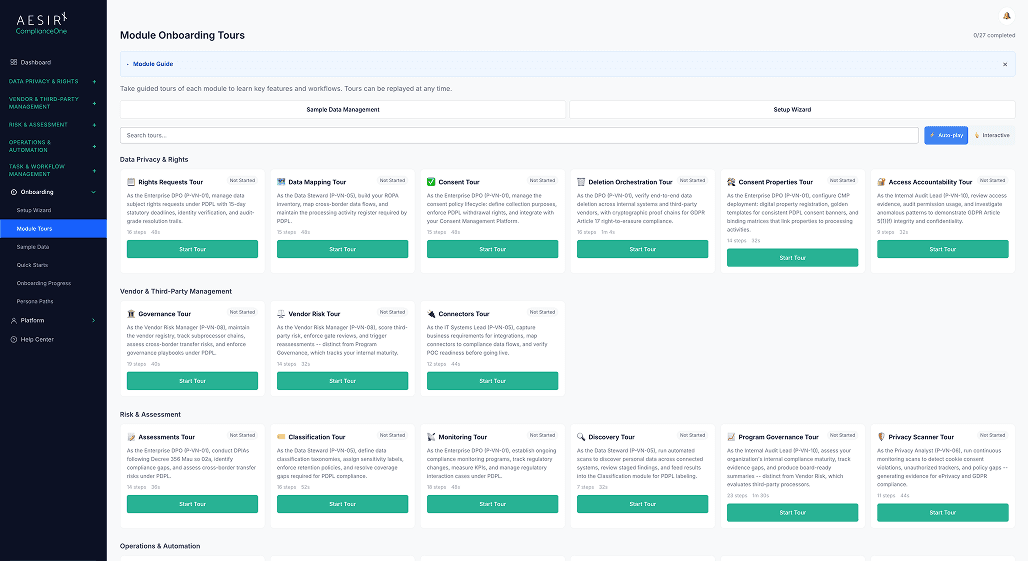
None of the records below is an official form. Each is built on an internal template that the Law 23 record carries, and you keep it in one of two registers under Payments & eKYC Evidence:
Report-timing procedures for the Article 37 periods come with them, and the case due dates read their durations. The Law 23 record and its templates stay marked upcoming until commencement on 1 December 2026. You can use both registers before then.
Once Law 23 is added to your workspace as directly applicable, it appears beneath the Anti-Money Laundering Law as upcoming, effective 1 December 2026. Decision 1842 appears beside it as a reference record with no requirements. Two registers appear under Payments & eKYC Evidence: AML Programme and Suspicious-Activity Cases.
Your scope, decided by a person.
The Scoping tab records whether you are a licensed provider, an applicant, a bank serving providers or not a reporting entity. It keeps the licences that role rests on, the basis, who determined it, who reviewed it and when. Each new determination is kept beside the ones it replaced. If you record that you are not a reporting entity, you give the reason, and the rest of the programme shows that reason instead of offering new records.
Your detection, written down.
The Indicator coverage tab lists each indicator the installed Law 23 record declares. For each one you record the method, the data relied on, the threshold your team chose and the owner, or that it does not apply and why. An indicator you do not cover yet can be recorded as not yet covered rather than left blank. A configuration version can be approved only when every indicator has a disposition, and each approval is kept as it stood. Your own indicators sit beside them, each with the date you notified the State Bank, or marked as notification not recorded.
Cases your team decides.
A case in the Suspicious-Activity Cases register holds what an investigation looked at: the wallet addresses and linked accounts, the indicators that raised it and the evidence, held as references to your own systems. The determination starts empty, with nothing suggested or scored. Only a person you have granted the right records it, with a rationale. Under your two-person rule, which stays on until your organisation records otherwise, the person who recorded the determination cannot approve it. Once approved, the case records the time, channel and reference of the report your team filed. Your team makes the call and files the report.
Two dates, and the Law does not choose.
Each case shows its Article 37 due dates, worked out only from the dates your team recorded and the periods the Law 23 record states, in your own working-day calendar. The 3-day and 1-day dates are both shown and neither is marked as the one that governs. With no detection time recorded, the detection-based date reads not recorded. The 24-hour date appears only for a customer-requested transaction showing signs related to crime, with a crime-linked detection time recorded. Until 1 December 2026 each date is labelled as applying from that day. The time you record for the report sits beside the dates as a value; lateness is not judged.
Restricted by default.
Only people you grant the case read permission see the register; others do not see the menu entry, a case, or its audit events. Every read is kept in the audit trail. A due-diligence refresh asked for from a case is recorded on the due-diligence record without naming the case.
Owners, launches and follow-on texts.
Beneficial owners are recorded against a due-diligence record from eKYC Evidence by your own references, with no names or identity numbers stored. A launch record for a new product, listing or feature cannot be approved until a person records it out of scope, or a linked risk assessment permits the launch with a decision dated before the launch date. Those conditions are your organisation's control: the Law requires the risk assessment before the product is offered and states no lead time. Each refusal cites the requirement the assessment serves. The Guidance tracking tab shows the follow-on texts Decision 1842 names, with when each was last checked; Decision 1772 reads as issued, with the Law 23 texts it lists.
An inspection pack on request.
For any period you choose, export the scoping record, the approved indicator configurations and the register of report references as CSV, XLSX, PDF or DOCX. The same period gives the same file. Case narratives are included only when a person with the approval right chooses to.
Due diligence you can show.
On the eKYC Evidence page you keep every verification attempt, failures included, and each due-diligence record linked to the obligation it discharges. A record linked to no obligation shows as a gap. The Investor Verifications register holds the account-opening evidence for the crypto-asset market pilot and links to those records without copying personal data.
Beside the crypto-asset market records.
Account Data Disclosures, Regulatory Disclosures, Sector Licences and Marketing Approvals already hold the Decree 284 evidence. Once Decree 284 is added to your workspace, inspection and information requests can be tracked on Authority Directions with their receipt evidence; the deadline is the one the request states.
What it does not do. ComplianceOne does not monitor transactions, analyse blockchains, screen against lists or decide that anything is suspicious. It connects to no State Bank system and submits nothing.
Keeps your reporting-entity scoping, the records-retention scope, indicator coverage approved as versions, beneficial owners by reference, the launch gate and the follow-on texts being tracked
Keeps each case, the determination a named person recorded, its approval, both Article 37 due dates and the reference of the report your team filed, visible only to the people you grant
Reads the records-retention scope you record on AML Programme instead of asking for it again
Keeps every verification attempt with its method, outcome and lawful basis, and each due-diligence record linked to the obligation it discharges
Records a conflict between two duties you owe, such as retention against disposal, and the person who decided it. It is never a verdict about a customer
Holds account-opening verification evidence for the crypto-asset pilot, with a reference to the due-diligence record
Once Decree 284 is added, keeps receipt and response evidence for inspection and information requests, with the deadline the request states
Shows the Decree 284 anti-money-laundering fine area with its article, once Decree 284 is added to your workspace
If you are preparing for 1 December 2026, confirm that:
See the AML Programme and Suspicious-Activity Cases registers with test data. Walk your indicator coverage to an approved version, and a case through a named person's determination and approval to the report reference, with both Article 37 due dates and the due-diligence evidence behind it.
Ronni K. Gothard Christiansen - Technical Privacy Engineer & CEO
Technical Compliance Expert, 32+ Years Open Source Advocate, X-BoD Open Source Matters Inc.
Law 23 itself takes effect on 1 December 2026, having been passed on 24 August 2026. Existing crypto-asset AML duties under Resolution 05/2025/NQ-CP already apply; do not wait for Law 23 to begin complying. Decision 1842/QĐ-TTg, the implementation plan, does not change that date. A Resolution of the National Assembly also carries the number 23/2026/QH16; laws and resolutions are numbered separately, and this is the Law.
Yes. The AML Programme and Suspicious-Activity Cases registers work now. The Law 23 record stays upcoming until 1 December 2026, and until then each due date on a case is labelled as applying from that day.
No. The Law reaches a financial institution licensed to provide crypto-asset services. A business that uses blockchain, or a person who holds crypto-assets, is not made a reporting entity by Law 23.
No. You configure your own detection, your team reaches the reasonable-grounds determination by its own analysis, and you file the report yourself. ComplianceOne records the rules, the case, the decision and the report reference. It is not a transaction-monitoring or blockchain-analytics tool and has no connection to the State Bank.
The Law lists the documents accepted for verification and admits other reliable sources that you must judge. It does not say that any decentralised identity, wallet attestation or analytics result satisfies the duty. ComplianceOne records the source you relied on and who accepted it; that judgement stays with you.
Law 23 states none. Anti-money-laundering failures in the crypto-asset market are sanctioned under Article 13 of Decree 284/2026/NĐ-CP, at 80 million to 200 million VND for an organisation, and an individual pays half. ComplianceOne shows that range with its article on Penalty Readiness once Decree 284 is added.
None is packaged. No Governor's regulation under the amended Article 26 (Law 23 Article 2(8)) had been published when checked on 26 September 2026. The State Bank's existing reporting rules under Law 14/2022 are not packaged, so the channel is free text and no form is modelled. ComplianceOne records the reference and dates of the report your team filed itself.

Map your detection rules against the fifteen indicators, walk one test case through to a reporting decision, and see where your due-diligence evidence has gaps.

Review your licence scope, your indicator coverage and your case procedure before 1 December 2026.

The evolution of Aesir is Aesir +  (the Norse symbol for Necessity)"Needed in order to achieve a particular result"
♥Join the AesirX Privacy Newsletter. Stay Informed. Stay Compliant.
 Audit Trail